An audit trail records what the agent did: each prompt, reasoning step, tool call, data access, and action, with timestamps. When that trail is complete, any decision can be reconstructed and reviewed after the fact, which is the foundation of incident response, dispute resolution, and regulatory inquiry.
Storage alone is not governance. Without a named owner, retention rules, and a review process, logs accumulate but nobody can answer who is accountable when an agent acts incorrectly. A reconstructable trail is what stops 'the agent decided' from being a defense, and governance is what keeps the trail trustworthy over time.
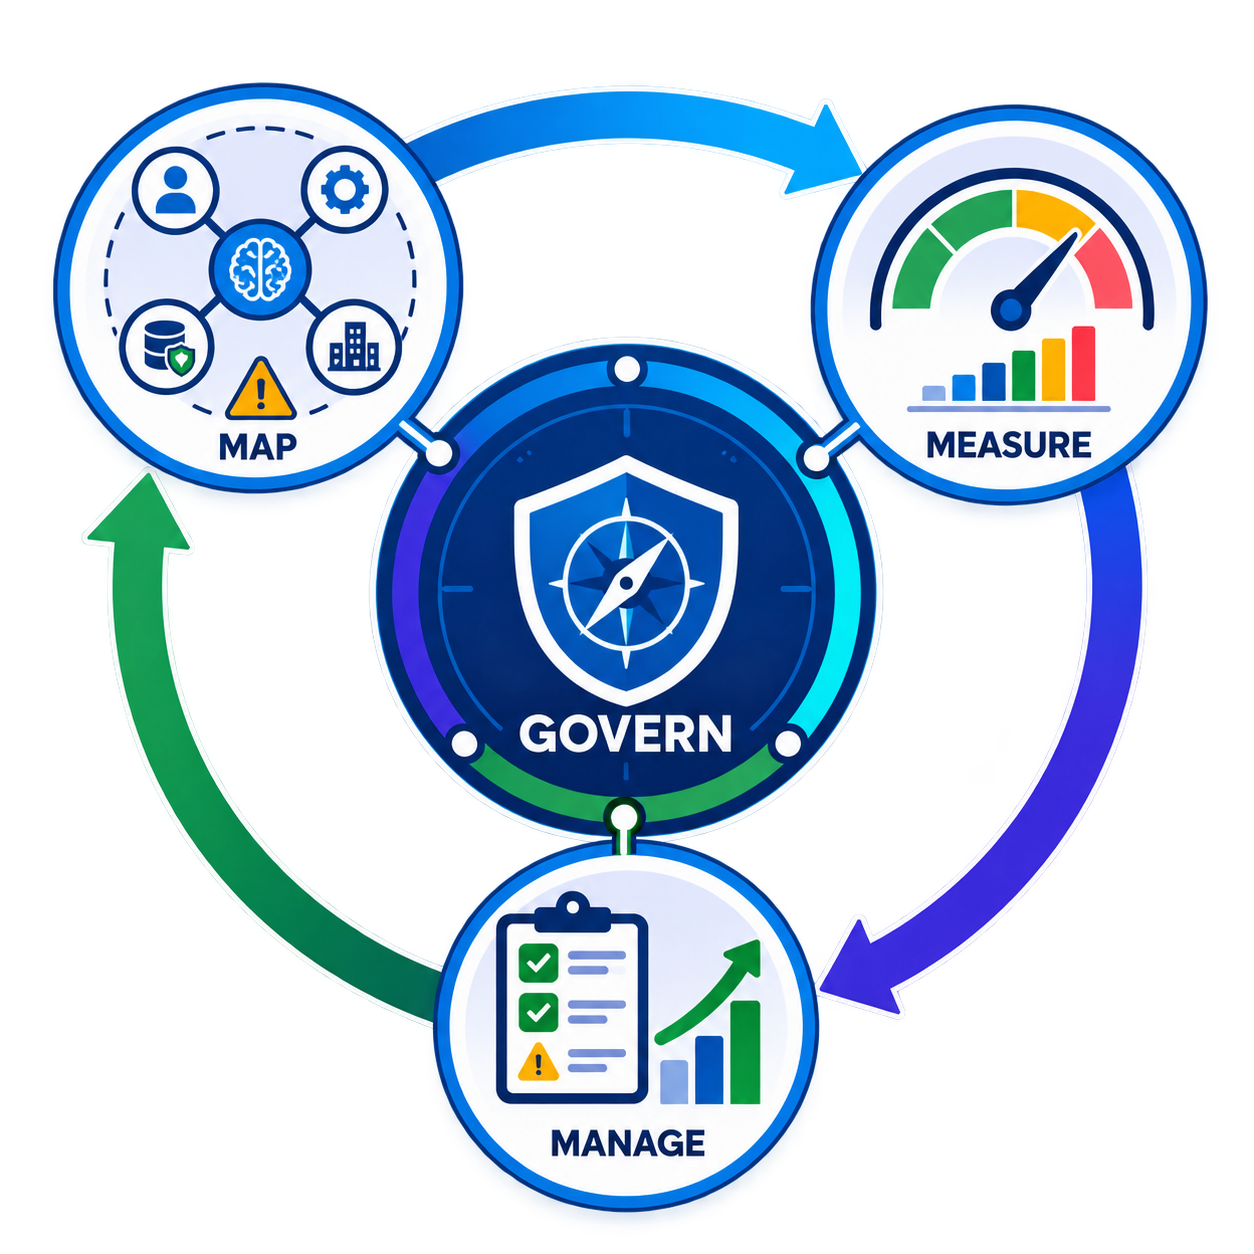
Treat the trail as a governed record
- Every step the agent takes must be timestamped and attributable to a session, user, and agent version.
- The trail must be reconstructable, meaning a reviewer can replay what the agent saw, decided, and executed.
- A named owner is accountable for trail completeness, access, and retention, not just for log storage.
- Access to the trail is itself controlled and logged, since it can contain sensitive customer data.
Assign ownership and verify coverage
- Use Agentforce session tracing and analytics to capture per-step detail, and confirm no action type falls outside the trail.
- Name an owner, typically in operations or compliance, and document the review cadence and escalation path.
- Define retention, access, and tamper-protection policies aligned with your regulatory obligations.
- Run periodic reconstruction drills: pick a past session, and prove a reviewer can fully explain the outcome from the trail alone.
Resources
This article is based on the following Salesforce learning and product documentation.