Prompt injection, bias, misuse, and privacy probes are how attackers and edge cases find the gaps in your guardrails before users do. An agent that grounds on CRM records and takes actions can expose data or execute steps far beyond a bad answer. Testing these scenarios once is not enough; each result needs a recorded outcome, a severity, and a named owner.
Hallucination can be minimized with grounding, topics, and the Einstein Trust Layer, but it cannot be eliminated. Governance covers the gap: when residual risk is documented, someone accountable has accepted it, and regression evidence exists for every material change to instructions, topics, actions, or data.
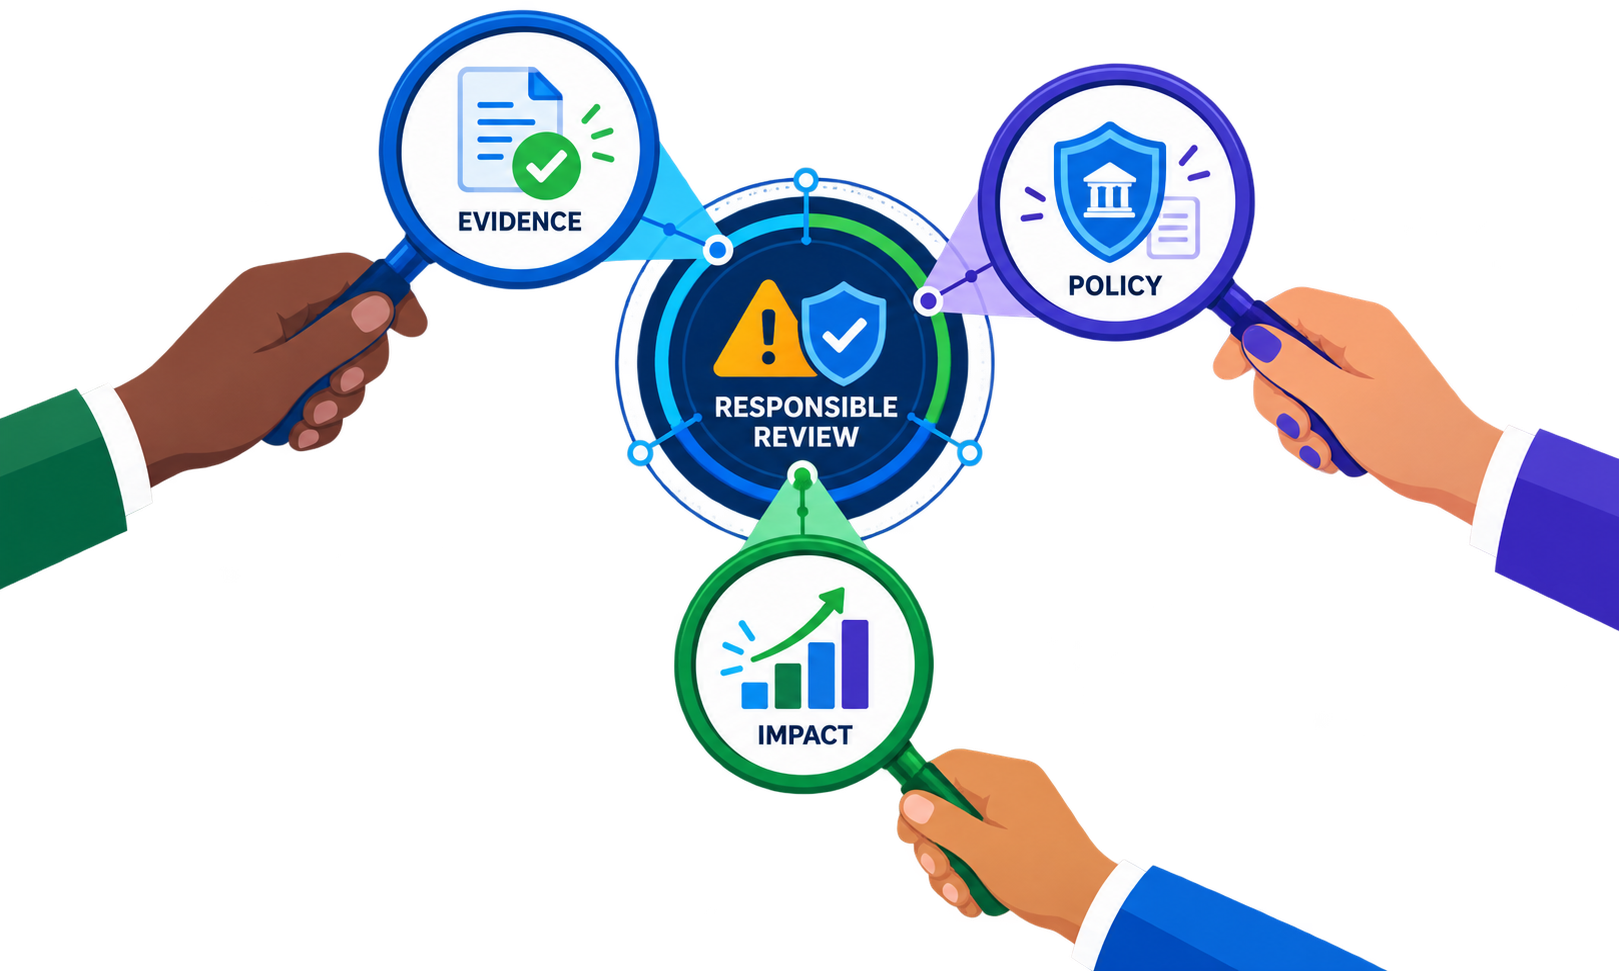
Test what the agent may access
- Probe injection attempts, off-topic steering, prompt leakage, and requests outside the agent's assigned topics.
- Test bias and fairness with representative user groups, phrasings, and demographic variations of the same request.
- Exercise misuse paths: bulk data extraction, cross-record access, and actions chained together beyond intended authority.
- Verify privacy controls by attempting to surface PII, masked fields, and data the running user should not see.
Keep evidence on record
- Build a scenario library in the Agentforce Testing Center covering each risk class, and run the full suite before launch.
- Log every outcome with expected versus actual behavior, severity, disposition, and the accountable owner.
- Re-run the full suite after every change to prompts, topics, actions, guardrails, or connected data sources.
- Track unresolved findings to closure, or to explicit and documented risk acceptance, before the next release.
Resources
This article is based on the following Salesforce learning and product documentation.